Chapter 19: Code Review Automation
AI-Powered Code Review
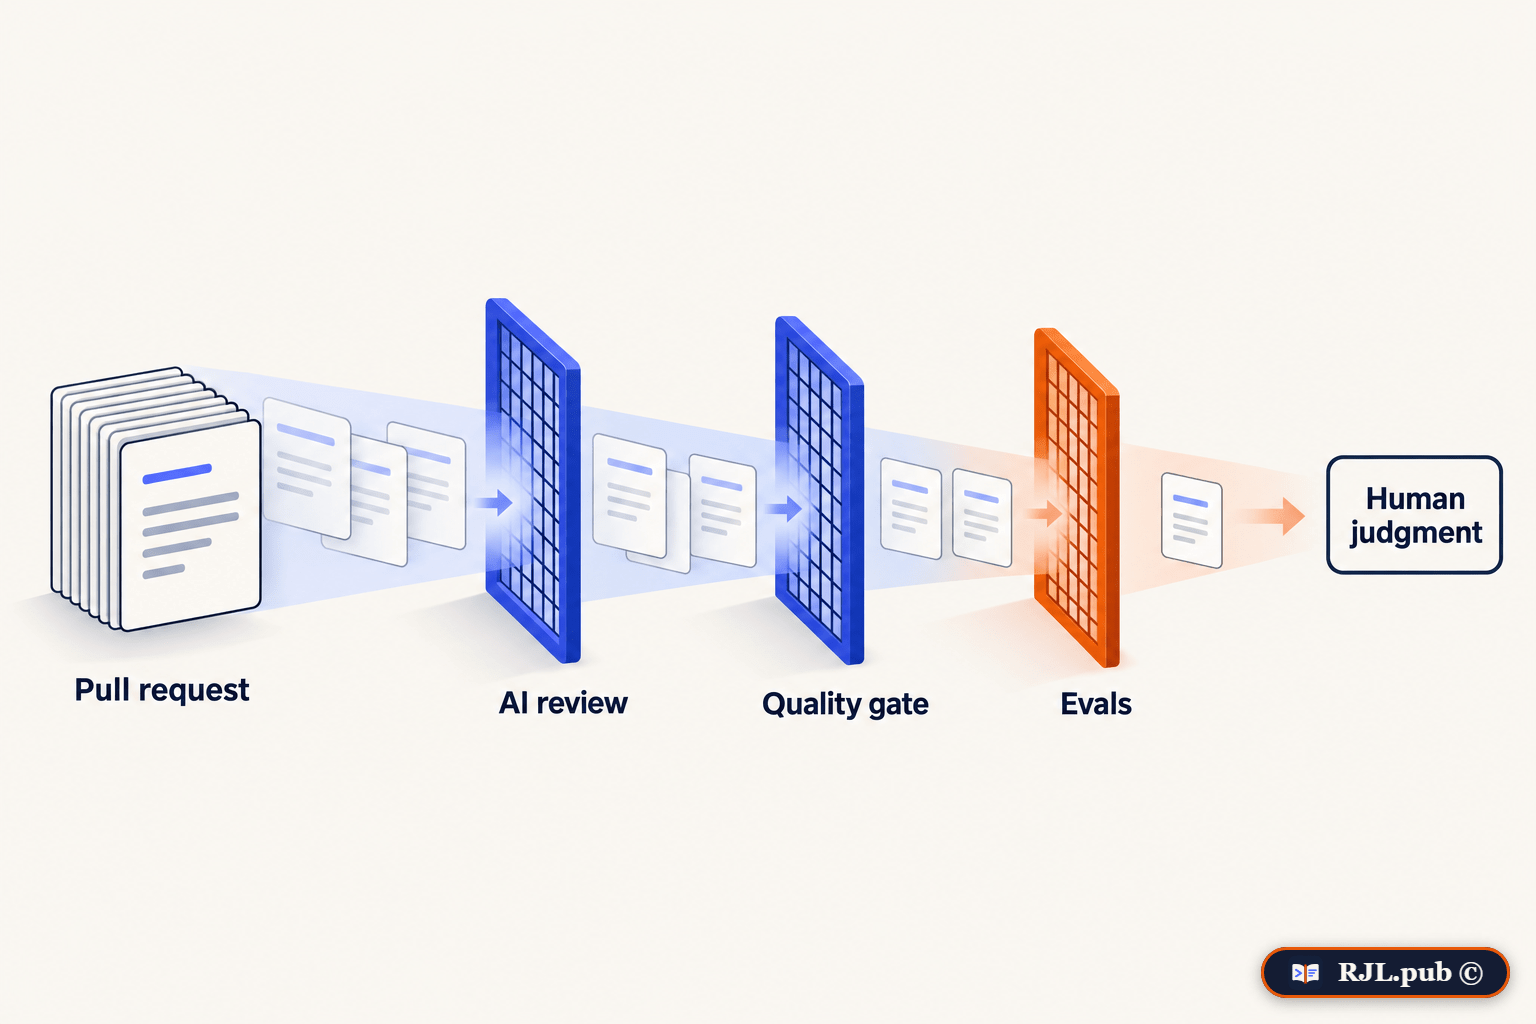
Agentic code review is one of the highest-ROI production patterns. Review agents check pull requests for style violations, security vulnerabilities, test-coverage gaps, and dependency issues before a human reviewer sees the diff. On real teams, a large share of routine reviews - on the order of 70% - is handled autonomously, freeing senior engineers for high-value feedback and lifting PR throughput without sacrificing quality.
# .github/workflows/ai-review.yml
name: AI Code Review
on: [pull_request]
jobs:
  review:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - name: AI Review
        uses: anthropics/claude-code-action@v1
        with:
          anthropic_api_key: ${{ secrets.ANTHROPIC_API_KEY }}
          prompt: "Review this PR for security, performance, and our standards in CLAUDE.md"
Review as a Quality Gate, Not a Rubber Stamp
The point of AI review is not to approve faster - it is to catch more before a human spends attention. Pair the review agent with hard gates: a static-analysis quality gate (such as SonarQube) that fails the build on regressions, and the eval suite that verifies the change met its intent. The human reviewer then spends their judgment on architecture and tradeoffs, not on catching a missing null check. AI augments quality; it does not own it. Self-reported success from the agent is not success - the gates are.